
Logging in through shared links
Description of the problem: I shared a post link I recently made to the Discord #thread-sharing, but was told by another user that they were briefly able to log in as me through that link.
Screenshot:
Device and browser used: shared link was produced on Phone, Firefox 136.0.2 (Build #2016079799)
Screenshot:
Reducio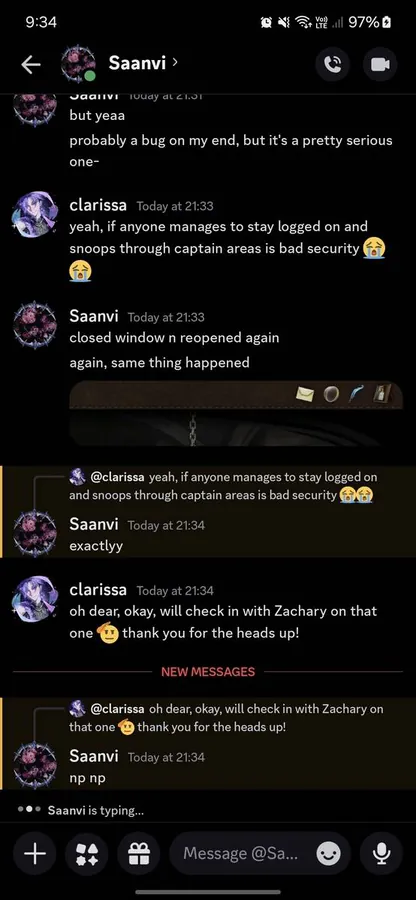
Device and browser used: shared link was produced on Phone, Firefox 136.0.2 (Build #2016079799)
“I hope she'll be a fool — that's the best thing a girl can be in this world, a beautiful little fool.”
― F. Scott Fitzgerald, The Great Gatsby
Logging in through shared links
Hello,
I think I know what happened. In some situations, where your browser is not configured to accept cookies, the site uses a parameter in the URL (?sid=xxx) to allow you to stay logged in from page to page. Otherwise, you would be constantly logged out.
The problem is that if you send a link with this identifier, the person who receives it could be logged in as you. To limit this risk, the site used to compare the first block of the IP: if it is the same, it considers it to be the same person, and if not, it does not make the connection. I think in this case, you happened to have a similar IP address.
I have just strengthened the protection to the maximum: it will now only work if you have exactly the same IP. This means that if the IP from your ISP changes, people who do not have cookies will be logged out. If I get a lot of complaints, I will test an intermediate setting...